An AWS environment that survives a NIS2 audit and staff turnover.
In four to eight weeks I separate test and production, move sign-in to your company account and make every change traceable. You get evidence for management and auditors, and your team gets an environment it can maintain itself.
References: Builders & Creatives, Property management software
- 4 weeks
- until test and production are separatedinstead of one account for everything
- 23 → 2
- people with admin rightseveryone else gets exactly the access they need
- 100%
- of changes traceablethrough code, review and audit log
- 1 day
- to produce the NIS2 audit evidencedown from two weeks of searching
Does this sound familiar?
For companies already on AWS, but with one account for everything, shared logins and no clear line between test and production.
- One account for everything
- Test, production and experiments all run in the same account. A mistake in test can hit production.
- Shared logins
- Several people use the same logins, sometimes even the root account. Nobody can tell who changed what.
- NIS2 is knocking
- Since the German NIS2 implementation act came into force, many companies with 50 or more employees have to prove risk management and incident reporting. Management is personally liable.
- Permissions only ever grow
- Admin rights were handed out once to get things moving and never taken back. Former contractors often still have access.
What changes for you
- A mistake in test no longer takes production down.
- Anyone who leaves the company loses AWS access the same day.
- After an incident you can see who changed what, even a year later.
- Contractors get exactly the permissions they need, and only for as long as they need them.
Where I have done this before
Builders & Creatives
12 accounts cleanly separated instead of one for everything
Designed and delivered an AWS target architecture with a multi-account setup end to end, from the first structure to running in production.
Property management software
Multi-tenant platform for property management on AWS: every organisation strictly isolated, the AI model inside the company's own AWS account, access and changes traceable.
Read the case studyTomislav designed and ran the AWS architecture behind our platform, from target architecture to production. Clear communication, solid execution, and infrastructure we can actually rely on.
 Sara KukovecCEO Builders & Creatives
How the AWS foundation project runs
The new structure is built alongside the old one. Your applications keep running, and at the end everything sits as code in your repository, so you are not dependent on me.
Discovery
A workshop with IT and the business teams. Which applications exist, who needs which access, which rules apply?
Design
Account structure, roles and network on a few pages, for you to sign off.
Build
I set up the structure, switch on logging and threat detection, and write everything as code.
Migration & handover
Your applications move over one at a time, to plan. Your team gets training and an operations manual.
What I need from you
- One contact person from IT or management
- One workshop day at the start, then roughly one short meeting a week
- Read access for the analysis, write access only for the build
Technical scope for your IT team
- Multi-account structure with AWS Organizations and Control Tower
- IAM Identity Center connected to Entra ID or Google Workspace
- Least-privilege roles, admin rights only for a limited time
- Organisation-wide CloudTrail with Object Lock, at least one year of retention
- GuardDuty, Security Hub and AWS Config in every account
- Service control policies and budget alerts per account
- AWS Backup with policies and a copy in a separate account
- Terraform code and operations manual
Start small, then decide
Every step delivers its own result at a fixed price. You can start or stop at any point.
AWS security check
An online questionnaire on the controls that are most often missing in practice.
- Traffic-light rating across five areas
- Your biggest gaps, explained
- No access to your systems needed
Security quick scan
I review your environment with a read-only role and write down what to tackle first.
- Your ten biggest risks, ranked by urgency
- A concrete action for each risk
- 45-minute results meeting
Security review with NIS2 mapping
A review against the AWS Well-Architected Framework, mapped to the NIS2 requirements.
- A report you can hand to auditors
- Action plan with effort and sequence
- A briefing paper for management
AWS foundation
Separate accounts, sign-in with your company account, guardrails and audit logs, all as code in your repository.
- New projects get their own secured space in minutes
- Your team can maintain the environment itself
- Handover with training and an operations manual
All prices exclude VAT. "From" prices depend on scope and become a fixed price after the assessment.
You work directly with me
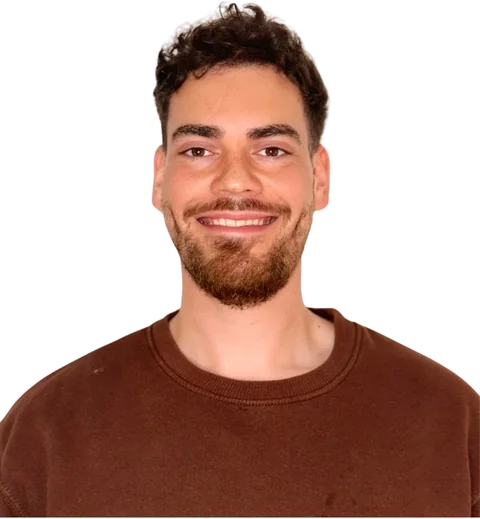
I'm Tomislav Pree, a cloud architect from Mainz. I have built and run cloud platforms since 2018, most recently for Builders & Creatives, in large scale e-commerce and in the aviation industry. From the first call to the handover you talk to the person who does the work.
Afterwards: Ongoing security support
Once a month I look over your environment, clean up permissions and keep the evidence up to date.
- Monthly review of security findings
- Permission reviews and offboarding
- Up-to-date NIS2 evidence
- A point of contact when incidents happen
What clients ask before they start
Do you need admin access to our systems for this?
For the quick scan and the review, a read-only role is enough. You create it yourself and can revoke it at any time. I only need write access to build the foundation, and only in the accounts involved.
Does NIS2 apply to us at all?
That depends on your sector, size and revenue. Many companies in the listed sectors with 50 or more employees or €10 million in revenue are affected. The binding assessment is a job for your legal advisers. I make sure the technical side in AWS meets the requirements.
Do our applications keep running during the rebuild?
Yes. The new structure is built alongside the old one, and applications move over one at a time, to plan. Where a short maintenance window is needed, we agree it in advance.
How much of our time will this take?
You need one fixed point of contact who can make decisions or get them made quickly. At the start and at handover that means a few hours a week, in between usually one short meeting a week. I do the actual work.
We have no cloud team of our own. Is that a problem?
No, that is the typical case. I build the environment so it needs little upkeep and train the people who will look after it. If nobody has the capacity, add the monthly support.
Where do you stand today?
16 questions, five minutes, no sign-up. You see straight away where your AWS environment stands and what to fix first.